

TECHNOLOGY ADVISORY FOR ACCOUNTING FIRMS
Know who is accountable for your firm's technology and cyber risk.
Get an independent view of where vendor responsibilities stop, what your accounting firm still needs to own, and what leadership should verify next—without being sold software, managed IT, or cybersecurity tools.
Request Consultation AvailabilityWe'll confirm fit and provide secure scheduling and payment options before requesting supporting materials.
Helpful to have ready: a high-level vendor list, your IT-support model, known concerns, and any existing policies or risk documentation. Please do not send client data, tax returns, account numbers, passwords, or credentials.
Led by Sterling Unan, CISSP — 25+ years in financial-services technology and operations · Independent, product-neutral advisory
Accounting Firm Technology & Cyber Risk Consultation
$495 fixed fee · 60–90 minutes
A leadership-level diagnostic—not a technical audit or penetration test.
A confidential consultation for firm owners, managing partners, and operational leaders who need a clearer view of technology accountability, vendor responsibility, and cyber risk.
Your consultation includes:
- A focused 60–90 minute leadership-level discussion
- An immediate Technology & Cyber Risk Snapshot
- A concise written Consultation Report within three business days
- Practical direction that can stand on its own
No obligation to change providers, purchase a broader review, or enter an ongoing advisory arrangement.
Beech Tree does not sell technology products, managed IT services, or cybersecurity tools.
VENDOR RESPONSIBILITY CHECKLIST
7 Questions Every Accounting Firm Should Be Able to Answer About Its Technology Vendors
If any of these questions are unclear, your firm has a gap worth addressing.
Not sure how your firm would answer these questions? That is exactly what an Accounting Firm Technology & Cyber Risk Consultation is designed to address.
Request Consultation AvailabilityYour current IT provider remains part of the solution. The consultation gives you clearer questions, ownership, and next steps.
WHAT YOU RECEIVE
What you receive
During the consultation
- A focused 60–90 minute leadership-level discussion
- An immediate Technology & Cyber Risk Snapshot
- Key concerns, accountability questions, and areas requiring verification
- Practical questions to take back to your IT, cloud, cybersecurity, tax-software, and other technology vendors
Within three business days
- A concise written Consultation Report
- A prioritized summary of observations and recommended next steps
- A clearer distinction between what is known, what needs verification, and what leadership should decide
- Practical direction that can stand on its own
- A partner-ready summary of priorities, ownership questions, vendor follow-ups, and recommended next steps.
This is independent technology and risk-management guidance—not a penetration test, technical audit, legal or regulatory opinion, formal compliance certification, product proposal, or managed-services sales conversation.
THE WHOLE PICTURE
Your technology vendors are not your technology strategy.
Your providers may each manage an important part of the environment, but no individual vendor owns the whole picture. Firm leadership remains responsible for understanding technology, cybersecurity, access, data protection, continuity, and vendor accountability together.
Managed IT provider
Devices, support, selected security operations, and day-to-day technology support.
Microsoft 365 and cloud platforms
Identity, email, collaboration, file storage, application infrastructure, and service availability.
Tax, accounting, payroll, document, and client-service vendors
Tax software, accounting platforms, client portals, document management, e-signature, payroll, payment, and workflow tools.
Your firm
Leadership, governance, client trust, risk decisions, and accountability.
This is especially important as firms adopt new cloud services, enable remote or hybrid work, use seasonal or contract staff, rely on interconnected third-party vendors, and evaluate AI tools. The goal is not to manage every technical detail internally. It is to know the right questions, assign ownership clearly, and make informed decisions.
Firm Risk Extends Beyond the Office
Remote work, home-office environments, personal devices, client portals, and AI tools used by staff or contractors can all affect the firm's technology and cybersecurity posture. Beech Tree's advisory covers the full operating environment—not just the office network.
INDEPENDENCE
Independent advice. Practical direction.
Independent perspective
Beech Tree does not sell technology products, managed IT services, or cybersecurity tools. Recommendations are not shaped by product quotas, implementation revenue, or vendor referral fees.
Built for firm leadership
The consultation is designed for firm owners, managing partners, administrators, and other decision-makers who need a clearer view of technology accountability and risk.
Actionable without pressure
The consultation stands on its own. There is no requirement to change providers, purchase a broader review, or enter an ongoing advisory arrangement.
EXPERIENCE
Experience that connects technology to firm leadership.
Sterling Unan, CISSP, brings more than 40 years of technology and cybersecurity experience, including more than 25 years supporting financial-services technology and operations. Beech Tree helps leadership teams translate technical complexity into practical questions, clearer accountability, and decisions that fit the firm's operating reality.
Led by Sterling Unan, CISSP, with 25+ years in financial-services technology and operations and more than 40 years of technology and cybersecurity experience.
Financial Services Technology & Operations
Experience supporting technology leadership, security, vendor relationships, business continuity, and the operational systems that support investment and client-service functions.
Accounting-Firm Risk Context
Practical understanding of the sensitivity of client financial and tax information, time-sensitive filing and payroll processes, third-party dependencies, and the trust requirements that shape accounting-firm relationships.
Cybersecurity, Governance & Resilience
CISSP-led cybersecurity experience, including identity security, Microsoft 365 governance, vendor oversight, backup and recovery, incident readiness, and business-continuity planning.
Independent Advisory Discipline
Experience improving vendor accountability, evaluating technology services, reducing unnecessary spend, and giving leadership practical information for better decisions.
Led by Sterling Unan, CISSP, with 25+ years in financial-services technology and operations and more than 40 years of technology and cybersecurity experience.
BROADER REVIEW OPTION
If a deeper review is needed
$495 Consultation
A focused, fixed-fee conversation that gives you immediate clarity on your most important technology and cybersecurity questions. It includes your immediate Technology & Cyber Risk Snapshot and a written Consultation Report within three business days.
Accounting Firm Technology & Cyber Risk Review
A comprehensive, independently scoped review of your firm's full technology and cybersecurity environment. Separately scoped and priced based on firm size, technology complexity, vendor relationships, and the questions leadership needs answered.
Some firms may decide they need a broader independent review after the consultation. If so, Beech Tree can discuss a separately scoped engagement focused on the firm's technology environment, vendor relationships, cybersecurity governance, and operational resilience. The initial consultation remains useful on its own, and the firm decides whether to proceed further. The initial consultation stands on its own. A deeper review is discussed only when leadership wants additional evidence, broader environmental visibility, or more detailed vendor-accountability analysis.
A full review typically includes:
- Complete technology-environment assessment
- Vendor accountability and contract review
- Client-data protection and nonpublic personal information alignment
- Microsoft 365 security, identity, and access-control review
- Backup, recovery, and business-continuity readiness
- Technology governance and strategic alignment
- AI adoption, policy, and data-protection review
Full reviews are separately scoped and priced after the initial consultation, only when additional detail would be useful to the firm.
What a Full Review Includes
- Written findings report with prioritized recommendations
- Vendor-accountability matrix for leadership
- Technology-risk summary for firm leadership
- Practical plan with vendor questions and next steps
EXAMPLE FINDING
Example finding
EXAMPLE: A SMALL ACCOUNTING FIRM
- The managed IT provider held administrator access to the firm's Microsoft 365 environment, including email, SharePoint, and client-document systems. Firm leadership had not confirmed whether it held emergency administrative access.
- The firm did not maintain a current inventory of privileged accounts, a documented process for reviewing vendor access, or a clear offboarding checklist for seasonal employees, contractors, and former personnel.
- Multi-factor authentication was not consistently enforced for all administrative and remote access. The IT provider confirmed MFA was enabled broadly, but the firm had not independently verified the scope or configuration.
- There was no documented plan for how staff would communicate with clients and continue priority tax, payroll, or filing-related work if email, a client portal, or a core cloud platform became unavailable.
Why it mattered:
Client information and communications were exposed to avoidable operational and cybersecurity risk. The concern was not that a vendor was acting improperly—it was that the firm could not independently verify or document accountability, access, and control performance in several critical areas.
Practical next steps:
Document privileged access and establish recurring access reviews. Confirm MFA enforcement scope with the IT provider. Create an access-transition checklist for seasonal and departing personnel. Establish a basic client-communication and work-continuity plan for technology disruptions during critical periods.
Illustrative example based on common patterns. The Snapshot distinguishes what is known, what is reported by firm leadership, what requires vendor confirmation, and what may warrant a separately scoped review. Details are generalized and do not describe a specific client engagement.
READY TO STRENGTHEN YOUR FIRM'S TECHNOLOGY AND CYBERSECURITY POSTURE?
Start with a focused, independent conversation.
Tell us the technology or cybersecurity question your firm needs to answer. We will confirm fit and provide secure scheduling and payment options before requesting any supporting materials.
$495 fixed fee · 60–90 minutes · Payment is collected when scheduling · No recurring contract
WHAT HAPPENS NEXT
- 1.Request consultation availability
- 2.Receive a secure scheduling and payment link
- 3.Meet confidentially for 60–90 minutes
- 4.Receive your Technology & Cyber Risk Snapshot immediately after the consultation
- 5.Receive a written Consultation Report within three business days
You do not need to change IT providers to work with Beech Tree. The consultation helps you understand your current environment, ask stronger questions, and make more informed decisions with the vendors you already have.
Immediate Deliverable: Your Accounting Firm Technology & Cyber Risk Snapshot
At the end of your consultation, you receive an immediate Snapshot summarizing your priorities, risks, options, and vendor questions. The Snapshot distinguishes what is known, what is reported, what requires vendor confirmation, and what may warrant a separately scoped review. Your written Consultation Report is delivered within three business days after the consultation.
View a Sample Consultation Snapshot →Request Consultation Availability
Tell us a little about your firm and the question you are trying to answer. We will confirm fit, scheduling options, and secure next steps.
INDEPENDENT TECHNOLOGY & CYBER RISK ADVISOR
Sterling Unan, CISSP, brings more than 25 years of direct experience in financial-services technology and operations, including technology leadership, security, vendor relationships, business continuity, and the operational systems that support investment and client-service functions.
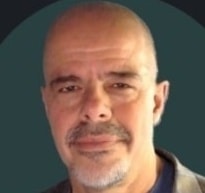
Sterling Unan, CISSP · Founder, Beech Tree Technology Advisors · 25+ years in financial-services technology & operations